20. Funding & Resources
LiveBuild a sustainable, current, source-verified funding strategy using total cost of ownership.
Learning objectives
- Connect a priority outcome to allowable funding candidates, lifecycle cost, local commitment, and a fact-check date.
- Use framework evidence and district context to explain a defensible priority or tradeoff.
- Record cost range, current allowable funding candidates, local share, sustainability, end-of-life plan, owner, and fact-check date.
Instructional cycle
Frame the decision → assess current practice → learn from the framework → practice → update the 90-day plan → brief leadership → reassess.
Applied practice: Funding Assumption Check
Identify claims that require verification or sustainability planning.
Topics in this Lesson
What you will be able to do
- Connect a priority outcome to allowable funding candidates, lifecycle cost, local commitment, and a fact-check date.
- Use framework evidence and district context to explain a defensible priority or tradeoff.
- Record cost range, current allowable funding candidates, local share, sustainability, end-of-life plan, owner, and fact-check date.
Opening dilemma
A failing security control competes with instructional priorities, while a one-time funding opportunity will not cover staffing or renewal. What should the request include?
Commit to a response before reading. Record the assumptions behind your choice.
Current-source note
The framework chapter is preserved as published, but funding rules are time-sensitive. The federal ARP/ESSER obligation deadline was September 30, 2024. Before relying on E-rate or another program, verify the current funding-year eligible-services list and program guidance. Do not assume a prior-year cybersecurity eligibility decision still applies.
U.S. Department of Education ARP/ESSER guidance · USAC current E-rate eligible-services lists
Pre-assessment
Before reading, rate the district’s current practice for this criterion: Funding requests are outcome-based, source-verified, lifecycle-aware, and sustained beyond initial purchase.
- Emerging — informal, reactive, or dependent on one person
- Developing — partly documented or inconsistently applied
- Operational — assigned, repeatable, implemented, and evidenced
- Leading — measured, rehearsed, integrated, and continuously improved
Securing adequate funding for cybersecurity initiatives remains one
of the most significant challenges facing K-12 districts. While the need
for robust cybersecurity protection has never been greater, many
districts struggle to allocate sufficient resources against competing
educational priorities. However, a variety of funding sources and
resource optimization strategies can help districts build effective
cybersecurity programs regardless of their budget constraints.
“E-rate has been essential for our cybersecurity infrastructure,”
notes Caroline Lightfoot, Director of Technology at Dickinson ISD.
“We’ve been able to implement robust network security measures that
would have been impossible with our limited budget.”
This chapter provides strategies for funding cybersecurity regardless
of district size, from leveraging federal programs to creative
partnerships and grant opportunities.
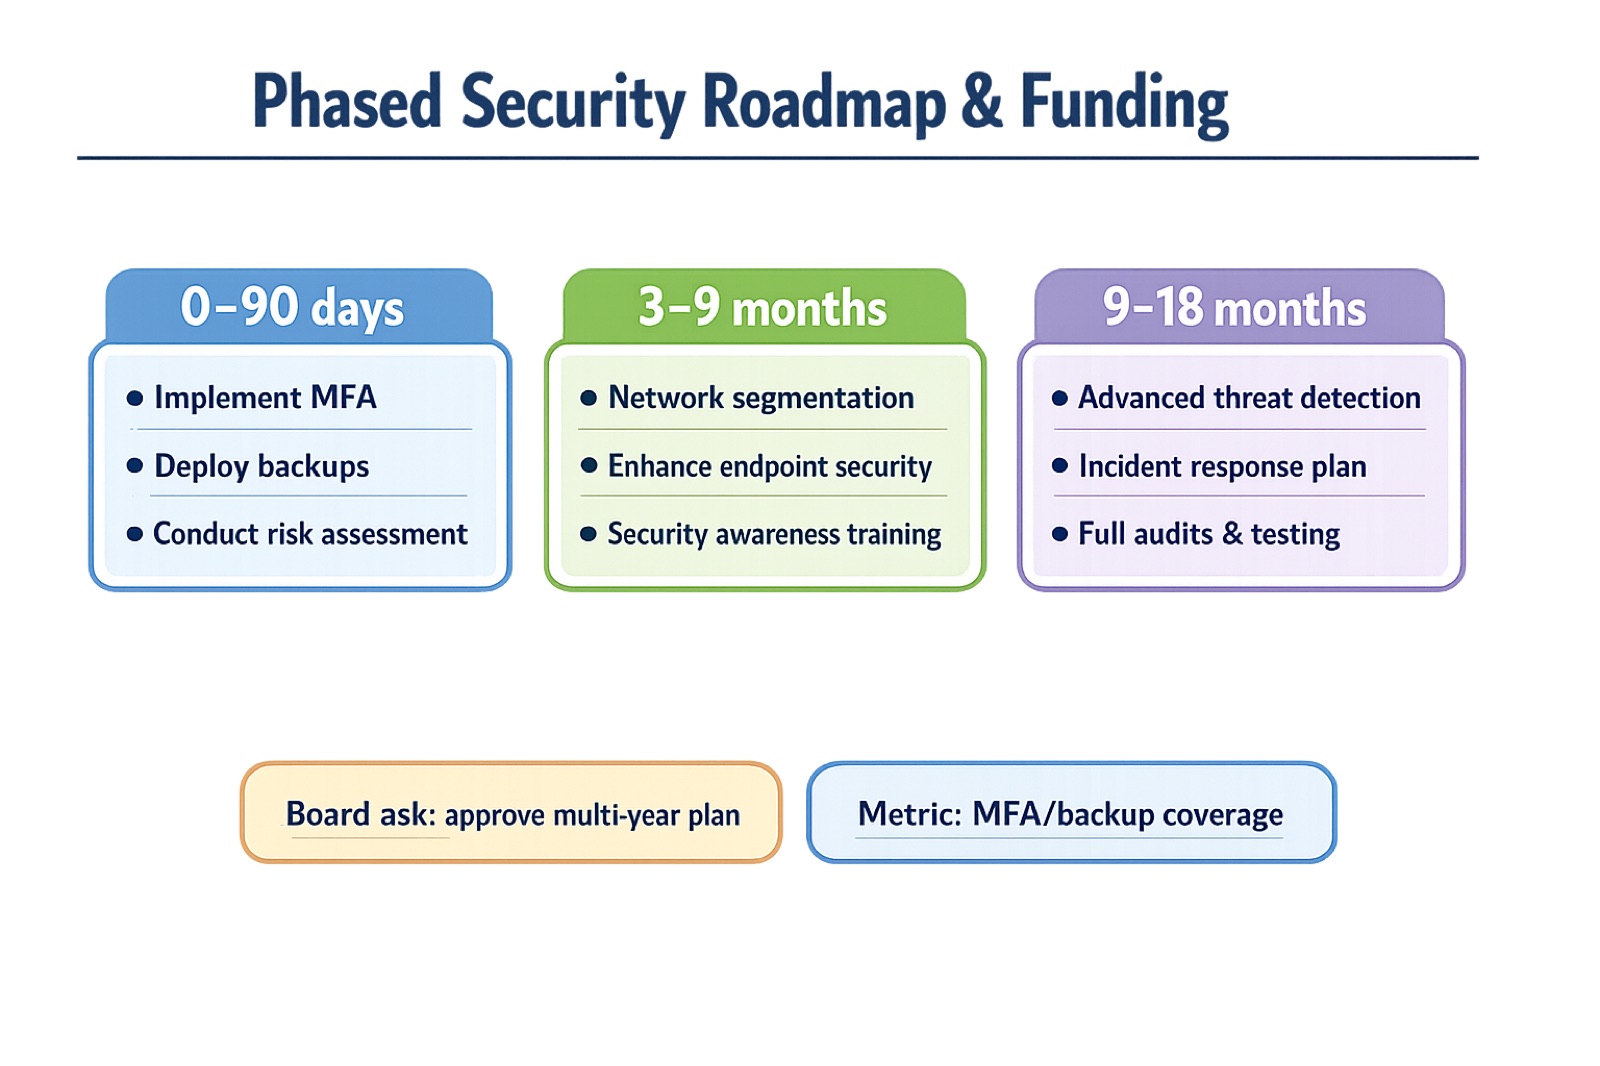
Figure: Three-phase funding strip with board ask and coverage
metric for quick approval conversations.
Rubric Checkpoint
NIST CSF Function: GOVERN
Rubric Domain: Oversight, Risk Management Strategy
NIST CSF 2.0 Categories:
| Category | Code | Outcome |
|---|---|---|
| Risk Management Strategy | GV.RM | Funding aligned with security priorities and risk tolerance |
| Oversight | GV.OV | Resource allocation monitored for effectiveness |
| Organizational Context | GV.OC | Funding strategy reflects district constraints and opportunities |
Sustainable cybersecurity requires sustainable funding. The Rubric
evaluates whether your resource strategy supports long-term security
goals.
Key Maturity Indicators:
- Level 2: Cybersecurity funded from general IT budget
- Level 3: Dedicated security budget line item
- Level 4: Multi-year funding plan; grant/E-Rate optimization
- Level 5: Dynamic funding tied to risk assessment priorities
Assessment Tip: The Rubric considers funding as part
of governance. “We don’t have budget” is a governance failure, not an
excuse. This chapter helps you find resources regardless of district
size.
The K-12 Funding Challenge
Budget Constraints
and Competing Priorities
K-12 districts face unique funding challenges that differ
fundamentally from other sectors. Unlike corporations that can allocate
dedicated cybersecurity budgets, school districts must balance
cybersecurity needs against competing educational priorities in an
environment of limited resources and increasing demands.
Most district budgets are allocated to core educational functions:
teacher salaries, classroom resources, and essential educational
programs. Cybersecurity initiatives must compete for the limited
discretionary funding that remains after these core needs are met.
Staffing
Limitations Compound the Challenge
The contrast between a Massachusetts district with 24,000 students
and 11 IT staff, and Dickinson ISD with 2,500 students and just 3 IT
staff, illustrates the dramatic variations in resources across
districts. These varying district sizes create dramatically different
funding needs and capabilities, requiring tailored approaches to
cybersecurity funding.
Regulatory
Requirements Create Both Challenges and Opportunities
FERPA compliance requirements create a legal mandate for
cybersecurity investment. State-specific regulations add complexity to
the compliance landscape. CIPA compliance requirements create
eligibility requirements for E-Rate funding, creating a direct
connection between compliance and funding opportunities.
E-Rate Program
The E-rate program provides critical funding for telecommunications
and information services in K-12 schools. While not specifically
designed for cybersecurity, E-rate funding can support many
security-related initiatives.
Category 1 Services
Category 1 covers telecommunications and internet access:
- High-speed internet connections with security features
- Wide area networks with secure connections
- Firewall services that protect network infrastructure
- Content filtering services (CIPA compliance)
Category 2 Services
Category 2 focuses on internal connections and basic maintenance:
- Network security appliances (firewalls, intrusion detection)
- Wireless access points with security features
- Managed switches with security capabilities
- Basic maintenance for eligible equipment
Strategic E-Rate Planning
Long-Term Perspective:
- Five-year planning cycles aligned with technology plans
- Phased implementation across multiple funding years
- Technology refresh planning for regular equipment replacement
- Budget optimization to maximize discounts
Compliance Requirements:
- CIPA compliance through internet safety policies and content
filtering - Documentation of E-Rate purchases and usage
- Audit preparation and ongoing compliance
- Policy development for funding eligibility
Maximizing E-Rate Benefits
Discount Optimization:
- Accurate reporting of free and reduced lunch data
- Consortium participation for increased purchasing power
- Competitive bidding for best pricing
- Including eligible professional development
Category 2 Management:
- Careful management across five-year cycles
- Equipment planning to maximize benefits
- Including maintenance and support in requests
- Technology integration with existing security infrastructure
Federal Grant Programs
ESSER Funds
The Elementary and Secondary School Emergency Relief (ESSER) program
provides significant funding for technology and cybersecurity
initiatives:
Eligible Uses:
- Technology infrastructure including network security
- Professional development for cybersecurity training
- Student data protection systems
- Remote learning security measures
Key Success Factors:
- Demonstrate clear need aligned with educational objectives
- Document impact on student learning
- Emphasize regulatory compliance and risk mitigation
“ESSER funding has been a game-changer for our cybersecurity
initiatives,” notes Dana Castine. “We’ve been able to implement
comprehensive security measures that protect our students and staff
while supporting our educational mission.”
CISA Grants
CISA offers various grant programs supporting K-12 cybersecurity:
State and Local Cybersecurity Grant Program:
- Funding for cybersecurity planning, assessment, and
implementation - Eligibility extends to state and local governments including school
districts - Multi-year funding available
School Safety Grant Programs:
- Comprehensive school safety funding including cybersecurity
- Technology integration support
- Training and awareness programs
Department of Education
Programs
Education Innovation and Research (EIR) Program:
- Supports innovative approaches including cybersecurity
- Research component for effective practices
- Scalability across districts
Supporting Effective Educator Development (SEED)
Program:
- Professional development and capacity building
- Cybersecurity training for educators
- Best practice sharing
State and Regional Funding
State Technology Programs
Many states offer dedicated technology funding supporting
cybersecurity:
Common Support Areas:
- Network security and infrastructure
- Professional development for cybersecurity training
- Security hardware and software
- Consulting services for planning and implementation
“State partnerships have been crucial for our cybersecurity program,”
says Mark Parsons of Inter-Lakes School District. “Through New
Hampshire’s MCDP program, we’ve been able to access training, resources,
and support that would have been beyond our reach otherwise. These
partnerships make cybersecurity achievable for small districts like
ours.”
Regional Educational
Service Agencies
RESAs often provide cybersecurity services and funding support:
Shared Services:
- Cybersecurity consulting and expert guidance
- Regional training initiatives
- Consortium purchasing for better pricing
- Shared technical expertise
Grant Administration Support:
- Assistance with applications
- Regulatory compliance support
- Coordination of resources
- Knowledge sharing facilitation
Private Foundation and
Corporate Funding
Technology Company Programs
Many technology companies offer grant programs for K-12
cybersecurity:
Microsoft Education Grants:
- Technology donations
- Training programs
- Innovation grants
- Partnership programs
Google for Education:
- Chromebooks and Google Workspace
- Built-in security features
- Professional development materials
- Innovation support
Other Technology Partners:
- Cisco Networking Academy
- Intel Education
- Dell Technologies
- HP Education
Cybersecurity Company
Programs
Security Awareness Programs:
- Free training for students and staff
- Educational resources and curriculum
- Competition support
- Mentorship programs
Technology Donations:
- Donated or discounted security software
- Security hardware and equipment
- Pro bono consulting services
- Professional development programs
Voices from the Field
Caroline Lightfoot, Director of Technology, Dickinson
ISD
“E-rate has been essential for our cybersecurity infrastructure.
We’ve been able to implement robust network security measures that would
have been impossible with our limited budget. The key is careful
planning and making sure every purchase aligns with both our security
needs and E-rate requirements.”
Mark Parsons, Director of Technology, Inter-Lakes School
District
“State partnerships have been crucial for our cybersecurity program.
Through New Hampshire’s MCDP program, we’ve been able to access
training, resources, and support that would have been beyond our reach
otherwise. These partnerships make cybersecurity achievable for small
districts like ours.”
Parsons also emphasizes strategic E-Rate planning: “E-Rate strategic
planning has been essential for our cybersecurity funding. We’ve learned
to integrate security components into our E-Rate applications, which has
allowed us to fund network security infrastructure that we otherwise
couldn’t afford. The key is careful planning and making sure every
purchase aligns with both our security needs and E-Rate
requirements.”
Dana Castine, Technology Director, Florida Union Free School
District
“ESSER funding has been a game-changer for our cybersecurity
initiatives. We’ve been able to implement comprehensive security
measures that protect our students and staff while supporting our
educational mission. The key is demonstrating how cybersecurity
investments directly support student learning and safety.”
Creative Funding Strategies
Resource Optimization
Phased Implementation:
- Implement based on risk and impact
- Spread investments over multiple years
- Test solutions before full deployment
- Use early successes to justify additional funding
Shared Services and Consortia:
- Collaborate with neighboring districts
- Pool resources for better pricing
- Share cybersecurity expertise
- Collaborate on training and development
Vendor Partnerships:
- Pilot programs to test solutions
- Educational pricing negotiations
- Value-added services
- Long-term relationship discounts
Alternative Funding Sources
Community Partnerships:
- Partner with local technology companies
- Engage parent-teacher organizations
- Apply for local foundation grants
- Leverage volunteer expertise
Student and Staff Programs:
- Student cybersecurity clubs
- Staff development investments
- Internship programs with colleges
- Mentorship with industry professionals
Grant Writing Strategies
Effective Grant Writing
Research and Preparation:
- Understand grant requirements and priorities
- Clearly articulate cybersecurity needs
- Align proposals with program objectives
- Involve key stakeholders in development
Proposal Development:
- Specific, measurable objectives
- Detailed, comprehensive budgets
- Realistic implementation timelines
- Methods for measuring success
Submission and Follow-up:
- Complete applications with all materials
- Professional presentation
- Timely submission before deadlines
- Follow-up communication
Grant Management
Compliance and Reporting:
- Ensure regulatory compliance
- Maintain accurate financial records
- Track progress toward objectives
- Measure and report impact
Sustainability Planning:
- Long-term planning beyond grant funding
- Integrate initiatives into ongoing operations
- Document successes for future requests
- Build partnerships for ongoing support
Implementation Roadmap
Phase 1: Assessment
and Planning (0-3 months)
Current State Analysis:
- Evaluate current cybersecurity funding
- Identify specific needs and priorities
- Conduct gap analysis
- Engage stakeholders in planning
Funding Strategy Development:
- Identify potential funding sources
- Prioritize based on likelihood and impact
- Develop application timelines
- Allocate resources for grant writing
Phase 2:
Application and Implementation (3-12 months)
Grant Applications:
- Develop comprehensive proposals
- Submit to identified funding sources
- Maintain funder communication
- Manage awarded grants
Implementation Planning:
- Detailed plans for funded projects
- Coordinate resources and personnel
- Manage timelines and milestones
- Ensure quality implementation
Phase 3:
Optimization and Sustainability (12-24 months)
Performance Monitoring:
- Measure and document impact
- Document successes and lessons
- Communicate results to stakeholders
- Identify improvement opportunities
Sustainability Planning:
- Plan for long-term funding
- Develop ongoing partnerships
- Share knowledge with other districts
- Plan for future funding needs
The Path Forward
Securing adequate funding for K-12 cybersecurity initiatives requires
creativity, persistence, and strategic thinking. While funding
challenges are real, numerous opportunities exist for districts to build
effective cybersecurity programs through a combination of federal,
state, local, and private funding sources.
The key to success lies in:
- Understanding available funding sources
- Developing compelling proposals aligned with funder priorities
- Implementing funded initiatives effectively
- Building sustainable funding relationships
- Sharing successes to justify continued investment
With the right approach, any district can secure the funding needed
to build effective cybersecurity programs that protect students and
staff while supporting their educational missions.
What Your Boss Should Know
The Bottom Line: Grant management requires
meaningful staff time but unlocks significant external funding,
substantially reducing local budget burden.
Board Decisions Required:
- Balance funding strategy across E-Rate, federal grants, state
programs, and private sources - Dedicate internal staff or hire grant writing specialists
- Leverage regional collaborations to improve funding
competitiveness
What Success Looks Like:
- Successful grant awards funding multi-year security
improvements - Significant reduction in local cybersecurity budget burden
- Sustained funding relationships for ongoing improvements
Why It’s Worth It: One successful grant funds
multiple years of improvements that would otherwise strain local
budgets.
Interactive Activity
Reflect
Which planned purchase has the least visible lifecycle or sustainability cost?
Apply the lesson
Record cost range, current allowable funding candidates, local share, sustainability, end-of-life plan, owner, and fact-check date.
Protect sensitive information. Use role titles and system categories. Do not enter student or staff records, credentials, network addresses, exploitable configurations, active incident details, or confidential vendor terms.
Interactive Activity
Build the boss brief
State the outcome being funded, full lifecycle commitment, and decision deadline.
Use five parts: risk; learning impact; proposed action; decision or support needed; evidence of success.
Post-lesson rubric reassessment
Funding requests are outcome-based, source-verified, lifecycle-aware, and sustained beyond initial purchase.
- Emerging — informal, reactive, or dependent on one person
- Developing — partly documented or inconsistently applied
- Operational — assigned, repeatable, implemented, and evidenced
- Leading — measured, rehearsed, integrated, and continuously improved
Use the same scale as the pre-assessment. Cite evidence of movement, or identify the next action if the rating did not change.