3. Resource Realities
LivePrioritize meaningful protection when staffing, time, and budget are limited.
Learning objectives
- Distinguish an essential control foundation from ideal-state work and defend a feasible sequence.
- Use framework evidence and district context to explain a defensible priority or tradeoff.
- Document essential controls, available force multipliers, one constraint, and the support needed to resolve it.
Instructional cycle
Frame the decision → assess current practice → learn from the framework → practice → update the 90-day plan → brief leadership → reassess.
Applied practice: Essential Before Ideal
Complete the resource-constrained sequence.
Topics in this Lesson
What you will be able to do
- Distinguish an essential control foundation from ideal-state work and defend a feasible sequence.
- Use framework evidence and district context to explain a defensible priority or tradeoff.
- Document essential controls, available force multipliers, one constraint, and the support needed to resolve it.
Opening dilemma
A small team can launch only two improvements this quarter. Several controls are valuable, but capacity is fixed. What comes first?
Commit to a response before reading. Record the assumptions behind your choice.
Pre-assessment
Before reading, rate the district’s current practice for this criterion: Resource planning matches commitments to real capacity and makes unabsorbed risk visible to leadership.
- Emerging — informal, reactive, or dependent on one person
- Developing — partly documented or inconsistently applied
- Operational — assigned, repeatable, implemented, and evidenced
- Leading — measured, rehearsed, integrated, and continuously improved
Small and rural districts face unique cybersecurity challenges with
limited staff, aging technology, and competing budget priorities.
However, effective security remains achievable through strategic
approaches that leverage collaborative resources, target available
funding, and prioritize no/low-cost controls.
“The biggest hindrance is often the sheer amount of work involved for
a small team,” notes Caroline Lightfoot, Director of Technology at
Dickinson ISD. “We have to be very strategic about how we allocate our
limited resources.”
This chapter doesn’t pretend you have enterprise-level resources.
Instead, it provides strategies that work within your actual constraints
while still achieving meaningful security improvements.
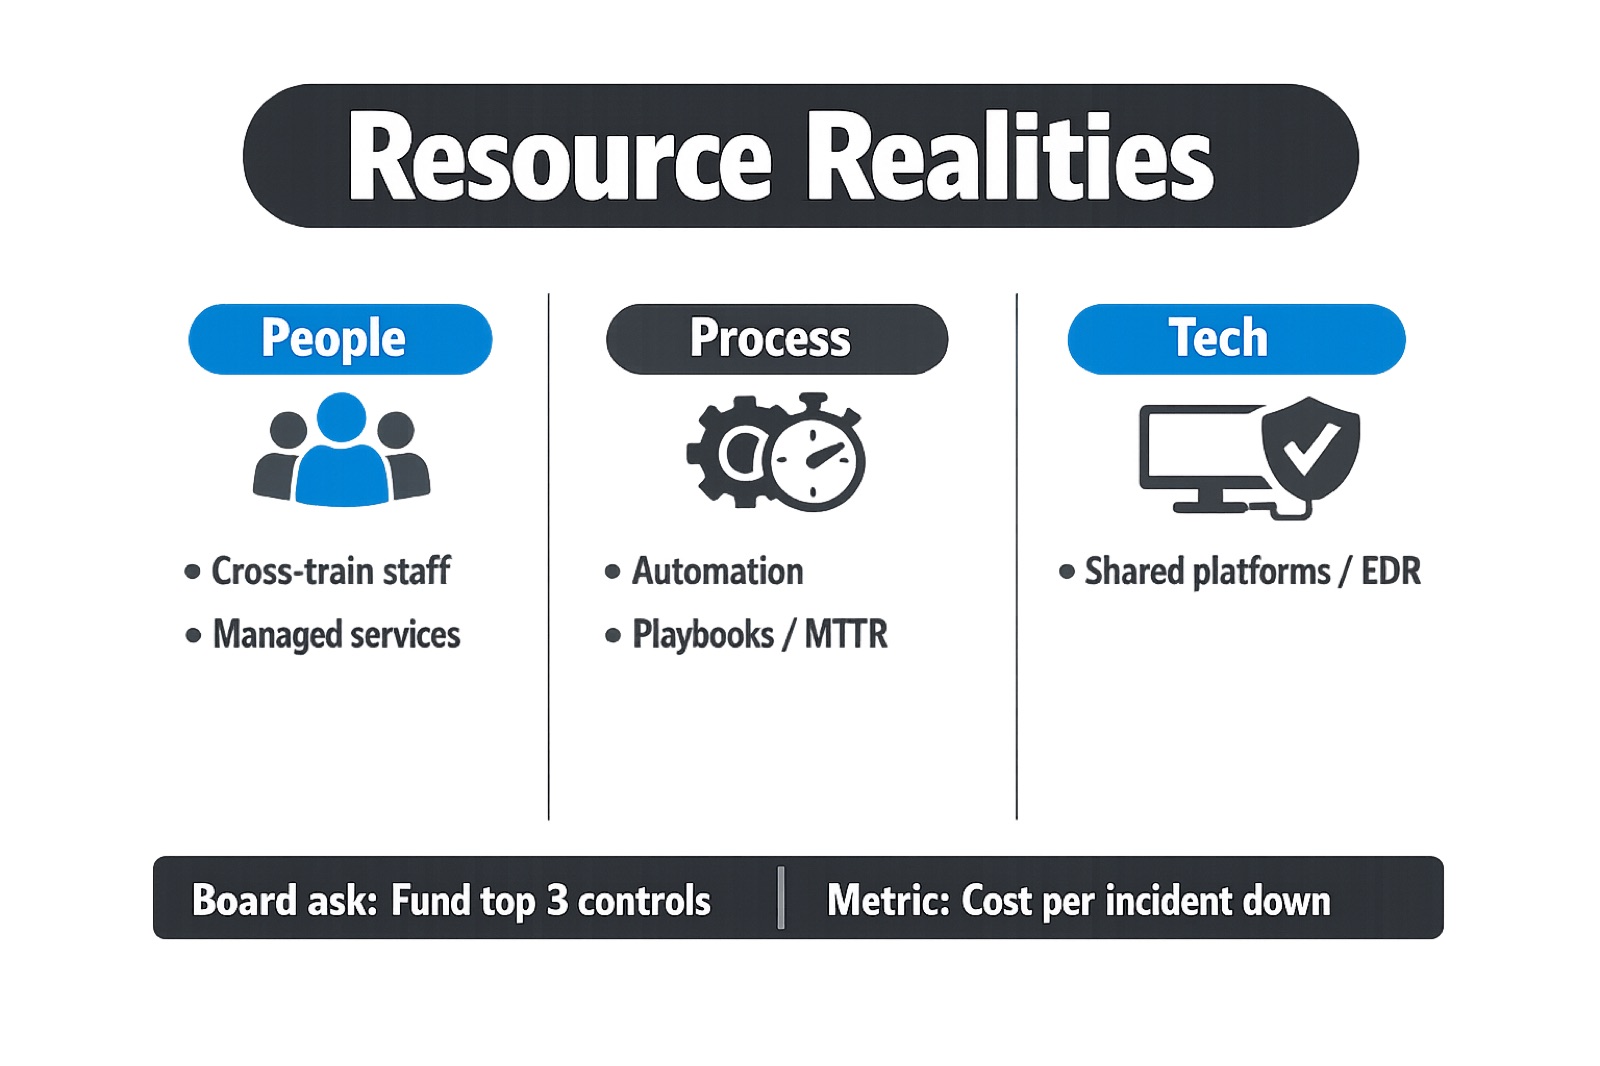
Figure: People/Process/Tech constraints with board ask and
cost/incident focus.
Rubric Checkpoint
NIST CSF Function: GOVERN
Rubric Domain: Risk Management Strategy, Oversight
NIST CSF 2.0 Categories:
| Category | Code | Outcome |
|---|---|---|
| Risk Management Strategy | GV.RM | Resource allocation aligned with risk priorities |
| Oversight | GV.OV | Leadership monitors security investment effectiveness |
Resource allocation is a governance decision. The Rubric evaluates
whether your district has a documented strategy for managing
cybersecurity within your specific resource constraints.
Key Maturity Indicators:
- Level 2: Basic budget line item for cybersecurity exists
- Level 3: Documented resource allocation strategy
- Level 4: Multi-year funding plan with board approval
- Level 5: Dynamic resource allocation based on risk assessment
Assessment Tip: The Rubric evaluates governance of
resources, not just the size of your budget. Small districts can score
well with clear strategies and creative partnerships.
The K-12 Resource Reality
The contrast between K-12 and corporate cybersecurity resources is
stark:
| District | Students | IT Staff | Ratio |
|---|---|---|---|
| Dickinson ISD | 2,500 | 3 | 833:1 |
| Large MA District | 24,000 | 11 | 2,181:1 |
| Typical Corporation | N/A | 1 per 50-100 employees | 50-100:1 |
These resource constraints mean that districts must be extremely
strategic about their security investments. Every dollar and every hour
of staff time must be directed toward maximum impact.
Staffing Models for
Cybersecurity
District Size
Recommendations
Small Districts (<1,000 students)
- IT Director with security responsibilities
- Part-time Cybersecurity Coordinator or MSSP support
- Leverage regional service center resources
Medium Districts (1,000-10,000 students)
- IT Director + Dedicated Cybersecurity Specialist
- Shared support staff
- Consider fractional CISO services
Large Districts (>10,000 students)
- IT Director + CISO or Cybersecurity Director
- 1-3 Security Analysts + external monitoring
- Dedicated incident response capability
Alternative Staffing
Approaches
- Shared resources between neighboring districts
through regional service centers or cooperatives - Third-party monitoring services (MDR) with K-12
specific expertise - Regional educational service center support (many
now offer security services) - Cybersecurity partnerships with local community
colleges or universities - Shared CISO models where multiple districts employ
a single security leader
Budget Planning
Typical Annual Costs
| Category | Typical Annual Cost |
|---|---|
| Basic Tools (MFA, backup, endpoint security) | 10−25 per user |
| Managed Detection and Response services | 12, 000−25,000 depending on size |
| Compliance Automation | 8, 000−20,000/year |
| External Security Assessment | 7, 500−15,000 (every 2 years) |
| Staff Training Programs | 3−10 per user per year |
| Incident Response Retainer | 10, 000−20,000/year (optional) |
| Data Privacy Compliance Tools | 5, 000−15,000/year |
Typical Small-to-Mid District Annual Budget: 50, 000−150,000 depending on scope and
maturity.
Cost-Sharing Opportunities
- Joint service agreements through educational service agencies
- Consortium purchasing through state education cooperatives
- Shared security services across multiple districts
- Leveraging existing state contracts for security tools
Practical
Strategies for Resource-Constrained Districts
1. Leverage Collaborative
Resources
Small districts can significantly enhance their security posture by
partnering with regional organizations and sharing resources.
Educational Service Centers and Regional IT
Cooperatives:
- Share specialized security staff across multiple districts
- Pool purchasing power for tools and services
- Access shared security expertise and training resources
Information Sharing Communities:
- Participate in K12 SIX or MS-ISAC communities specifically designed
for schools - Join K12Leaders Cyber Working Group for peer collaboration and
knowledge sharing - Access threat intelligence and best practices from peer
districts - Receive early warning about emerging threats and
vulnerabilities
State Education Agency Resources:
- Utilize state-level cybersecurity resources where available
- Access state-funded security assessments and training programs
- Participate in state-sponsored security initiatives
2. Target Available Funding
State-Level Cybersecurity Grants:
- Apply for state-level grants that often have set-asides for smaller
districts - Many states now offer specific funding for K-12 cybersecurity
initiatives - Focus on grants that support collaborative approaches
Strategic Technology Budget Allocation:
- Allocate portions of existing technology budgets for security
components - Frame security as essential infrastructure rather than optional
enhancement - Prioritize security investments that support educational technology
goals
E-Rate Category 2 Eligibility:
- Explore E-Rate funding for network security components
- Leverage E-Rate for firewall, filtering, and network monitoring
tools - Work with E-Rate consultants to maximize eligible security
investments
Cyber Insurance Premium Reductions:
- Use security improvements to negotiate better insurance terms
- Document security enhancements to demonstrate risk reduction
- Consider insurance requirements as justification for security
investments
3. Prioritize No/Low-Cost
Controls
Many effective security measures require minimal or no additional
funding.
Leverage Existing Platform Security:
- Enable free MFA capabilities in existing Google/Microsoft
subscriptions - Utilize built-in security features of current platforms
- Configure automatic updates for operating systems and
applications
Free Security Resources:
- Implement free basic security awareness resources from CISA and
MS-ISAC - Use K12 SIX Essential Cybersecurity Protections as a starting
roadmap - Access the K12Leaders Cybersecurity Framework and Cybersecurity
Rubric for comprehensive guidance - Join the K12Leaders Cyber Working Group for peer collaboration and
knowledge sharing - Access free security assessment tools and guidance
Built-in Security Features:
- Configure existing firewalls and network equipment for maximum
security - Enable logging and monitoring features already available in current
systems - Use free security tools and utilities available through educational
programs
4. Strategic Outsourcing
Focused outsourcing can provide enterprise-grade security without
enterprise costs.
Managed Security Services:
- Contract focused monitoring services rather than attempting
comprehensive coverage - Select providers offering education-specific packages with
FERPA/COPPA expertise - Focus on critical alert assessment to maximize internal staff
effectiveness
Virtual CISO Services:
- Consider virtual CISO services that provide fractional security
leadership - Access strategic security planning without full-time security
staff - Receive guidance on security investments and risk management
Regional Service Center Support:
- Many educational service centers now offer security services
- Access shared security expertise through regional partnerships
- Participate in regional security initiatives and training
programs
5. Community Engagement
Building a security-aware community can significantly enhance
protection.
Staff Security Awareness:
- Develop basic security awareness across all staff members
- Create clear incident reporting procedures
- Foster shared responsibility for digital safety
Local Technology Partnerships:
- Engage local technology businesses in volunteer security
initiatives - Partner with community colleges or universities for security
expertise - Access pro bono security assessments and consulting
Parent and Community Education:
- Provide basic security awareness information to parents
- Create clear communication channels for security concerns
- Build community support for security initiatives
Voices from the Field
Caroline Lightfoot, Director of Technology, Dickinson
ISD
“Our district serves about 2,500 students with a technology team of
just three people. We’ve had to be very strategic about our
cybersecurity approach. We started with the basics, enabling MFA on all
our administrative accounts and implementing automatic updates. These
free measures have provided significant protection without requiring
additional funding.”
Dan Klimke, Product Manager, NetAlly
“Especially in smaller districts, we’ve found that collaboration is
key. Participating in regional security initiatives and sharing
resources with neighboring districts enables access to enterprise-grade
security tools and expertise that they otherwise couldn’t afford on
their own.”
Dana Castine, Technology Director, Florida Union Free School
District
“We’ve been very creative about funding our security improvements.
We’ve used portions of our technology budget for security components,
applied for state grants, and leveraged our cyber insurance requirements
to justify security investments. Every incremental improvement has made
a meaningful difference.”
Mark Parsons, Director of Technology, Inter-Lakes School
District
“Small districts don’t need comprehensive security departments to
significantly reduce risk. We focus on essential hygiene measures,
strategic partnerships, and maximum utilization of existing resources.
The key is consistency and persistence.”
Implementation
Framework for Small Districts
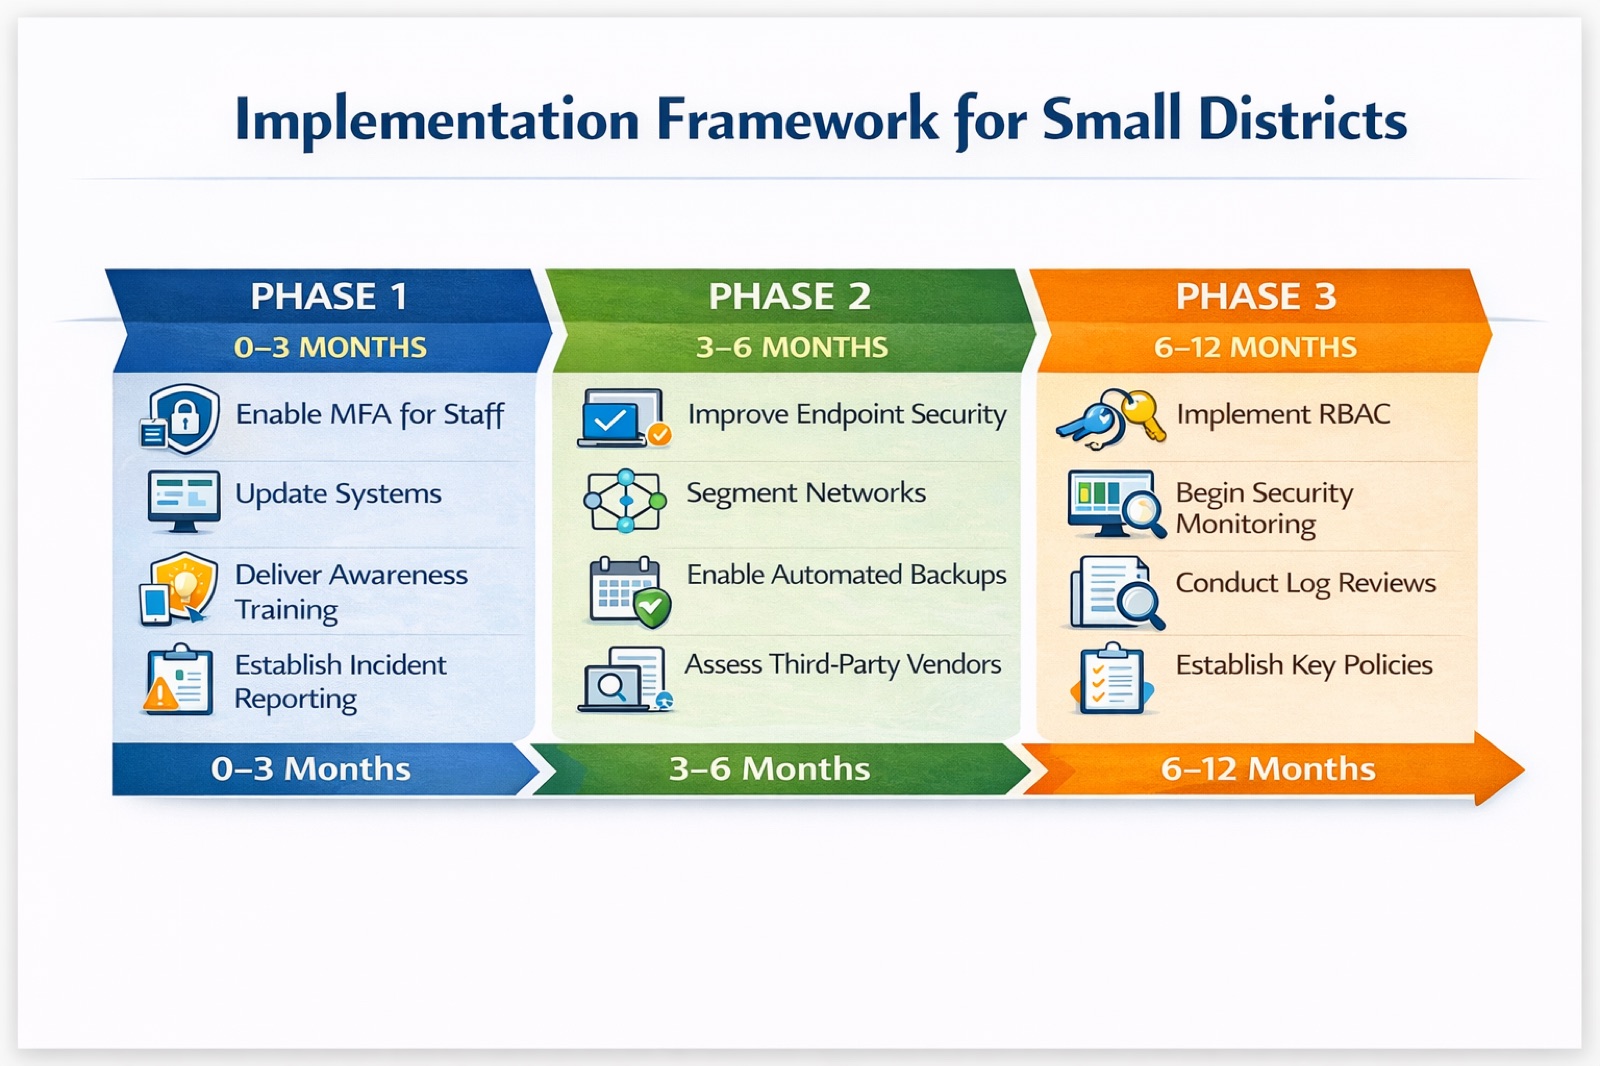
Phase 1: Foundation (0-3
months)
- Enable free MFA on all administrative accounts
- Configure automatic updates on all systems
- Implement basic security awareness training
- Create incident reporting procedures
Phase 2: Basic Protection
(3-6 months)
- Deploy free endpoint protection tools
- Implement basic network segmentation
- Establish backup procedures for critical data
- Develop vendor security assessment process
Phase 3: Enhanced
Security (6-12 months)
- Implement role-based access controls
- Deploy network monitoring tools
- Establish security log review procedures
- Create comprehensive security policies
Success
Metrics for Resource-Constrained Districts
Immediate Improvements (0-6
months)
- 100% MFA adoption on administrative accounts
- Automatic updates enabled on all systems
- Basic security awareness training completed
- Incident reporting procedures established
Medium-term Goals (6-12
months)
- Endpoint protection deployed across all devices
- Network segmentation implemented
- Backup procedures tested and verified
- Vendor security assessments completed
Long-term Objectives (12+
months)
- Comprehensive security policies in place
- Regular security assessments conducted
- Security metrics tracked and reported
- Security culture embedded in district operations
Key Success Factors
1. Start with the Basics
- Implement fundamental security measures that require minimal
resources - Focus on high-impact, low-cost controls
- Build on existing infrastructure and capabilities
2. Leverage Partnerships
- Collaborate with regional organizations and neighboring
districts - Access shared resources and expertise
- Participate in information sharing communities
3. Be Strategic About Funding
- Target available grants and funding opportunities
- Frame security as essential infrastructure
- Use insurance requirements to justify investments
4. Focus on People
- Develop security awareness across all staff
- Create clear procedures and responsibilities
- Build a culture of security consciousness
5. Measure and Improve
- Track security metrics and improvements
- Conduct regular assessments and reviews
- Continuously refine and enhance security practices
The Path Forward
Small districts don’t need comprehensive security departments to
significantly reduce risk. By focusing on essential hygiene measures,
strategic partnerships, maximum utilization of existing resources,
consistent staff practices, and practical compliance with educational
privacy requirements, even the most resource-constrained districts can
implement meaningful protections.
Every incremental improvement meaningfully increases protection for
students, staff, and community data. The key is to start with the
basics, leverage available resources, and build security capabilities
over time. With the right approach, effective cybersecurity is
achievable for districts of all sizes and resource levels.
The most important action is simply to begin: start with the
fundamentals, build on existing capabilities, and continuously improve
security practices. By taking a strategic, collaborative approach, small
and rural districts can achieve robust cybersecurity protection that
supports their educational mission while working within their resource
constraints.
What Your Boss Should Know
The Bottom Line: Resource-constrained security is
achievable with modest budget increases and prevents incidents that
would otherwise consume the entire annual IT budget.
Board Decisions Required:
- Choose partnership model: regional collaboration, shared services,
or managed security provider - Prioritize limited resources on controls with maximum risk
reduction - Pursue grant funding to offset local budget burden
What Success Looks Like:
- Basic cybersecurity hygiene implemented across all systems
- Enterprise-level protection through partnerships at small-district
pricing - Improved audit outcomes despite resource constraints
Why It’s Worth It: Small districts face
enterprise-level threats—one incident consumes a full year’s IT
budget.
Interactive Activity
Reflect
Which important security task is currently unrealistic without a new resource or leadership tradeoff?
Apply the lesson
Document essential controls, available force multipliers, one constraint, and the support needed to resolve it.
Protect sensitive information. Use role titles and system categories. Do not enter student or staff records, credentials, network addresses, exploitable configurations, active incident details, or confidential vendor terms.
Interactive Activity
Build the boss brief
State what can be reduced now, what needs investment, and what can responsibly wait.
Use five parts: risk; learning impact; proposed action; decision or support needed; evidence of success.
Post-lesson rubric reassessment
Resource planning matches commitments to real capacity and makes unabsorbed risk visible to leadership.
- Emerging — informal, reactive, or dependent on one person
- Developing — partly documented or inconsistently applied
- Operational — assigned, repeatable, implemented, and evidenced
- Leading — measured, rehearsed, integrated, and continuously improved
Use the same scale as the pre-assessment. Cite evidence of movement, or identify the next action if the rating did not change.